On 14 November 2026, our founder applied for Claude Mythos access from a personal paid Claude plan in Malaysia. About 20 minutes later, Anthropic's Verification Portal said "Defense Access approved". Before you copy us: Mythos is not a secret, smarter Claude, and for most businesses it changes nothing.
The short version: Mythos is not open to the general public. Apply to Anthropic's Cyber Verification Program (CVP) through its Verification Portal, on a paid Claude plan such as Pro, Max or Ultra. Individuals, including in Malaysia, can apply for Defense Access with a physical government photo ID.
Has Claude Mythos been released, and is it smarter than Fable?
Anthropic released Claude Fable 5.2 and Mythos 5.2 on 9 November 2026, the latest in the Fable line. The announcement is blunt:
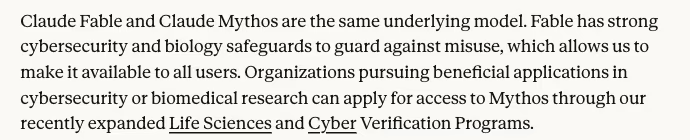 Anthropic's Fable 5.2 and Mythos 5.2 announcement, captured 15 November 2026.
"Claude Fable and Claude Mythos are the same underlying model. Fable has strong cybersecurity and biology safeguards to guard against misuse, which allows us to make it available to all users."
Source: Anthropic
The same page calls Mythos 5.2 "our most capable model for cybersecurity engineering", and adds that "Claude Fable 5.2's safeguards will block most cybersecurity-related tasks". So the difference is what each one agrees to do. Fable's filters stop high-risk work like penetration testing (a permitted, simulated attack on your own systems) and writing exploits. Mythos loosens those filters, within limits set by your tier.
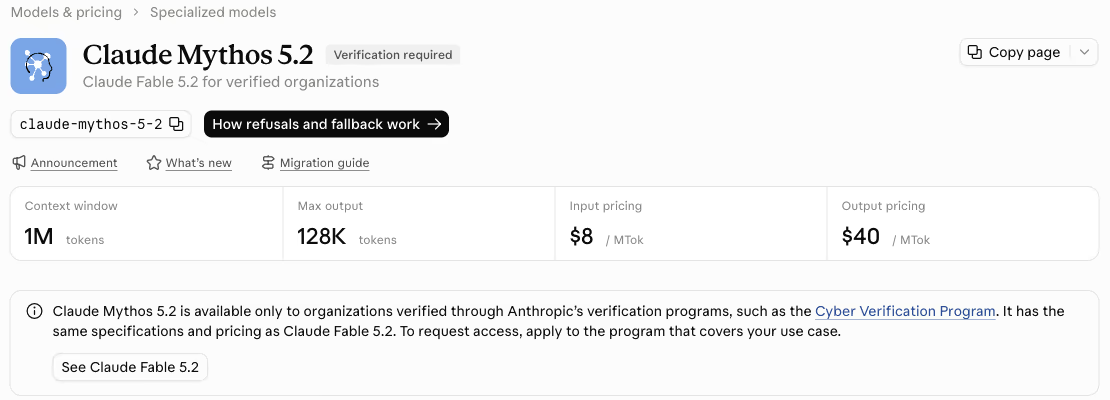 Anthropic's Mythos 5.2 docs page, captured 15 November 2026.
"Claude Mythos 5.2 is available only to organizations verified through Anthropic's verification programs, such as the Cyber Verification Program. It has the same specifications and pricing as Claude Fable 5.2."
Source: Claude Platform Docs
How do you get Claude Mythos access?
You need a paid plan (CVP "isn't available on the Free plan"), a physical government photo ID, and a phone camera for a possible live selfie, per Anthropic's Help Center.
Our founder applied as an individual for Defense Access, the defensive tier. The stated work: checking our founder's own web apps, servers and AI tools for new flaws, inspecting suspicious files, and writing fixes. No client systems.
It went in at about 11:13 pm Malaysia time and was approved by about 11:35 pm. Anthropic's target for Defense Access is two days, so don't plan around our 20 minutes.
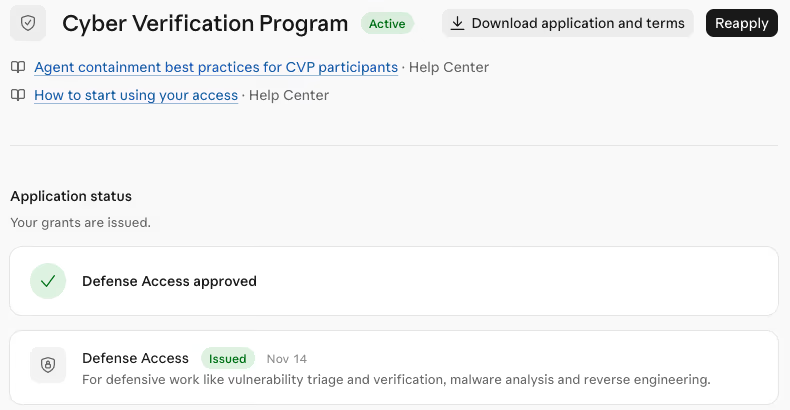 Our founder's Verification Portal after approval, captured 15 November 2026.
One snag in Claude Code: Mythos was missing from the /model menu at first. Typing /model claude-mythos-5-2 worked, and after a restart "Mythos 5.2" appeared in the list.
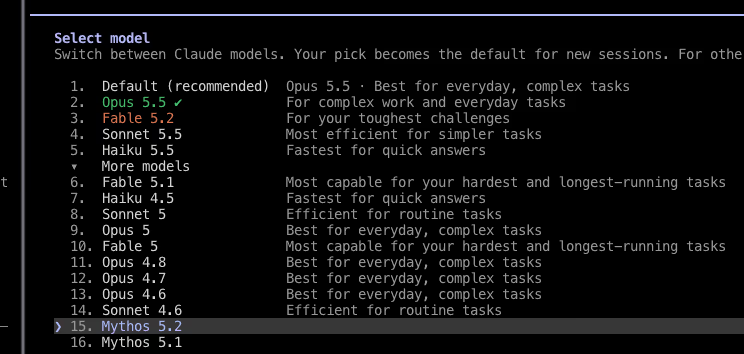 Claude Code's
/model menu after a restart, captured 15 November 2026.
The three tiers, per the Help Center. Individuals can only get Defense Access:
| Tier | What it covers | Who can apply | Target review |
|---|---|---|---|
| Defense Access | Malware analysis, incident response, checking and confirming flaws | Organizations and individuals, on any paid plan or the API | Two days |
| Red Team Access | Permitted penetration testing, exploit development | Organizations only, up to 75 users, on Team, Enterprise or API | Two weeks, currently longer |
| Specialized Access | Testing critical infrastructure | Organizations only, up to 25 users, on Team, Enterprise or API | No set target |
Do you need Claude Mythos access? What Malaysian businesses should know
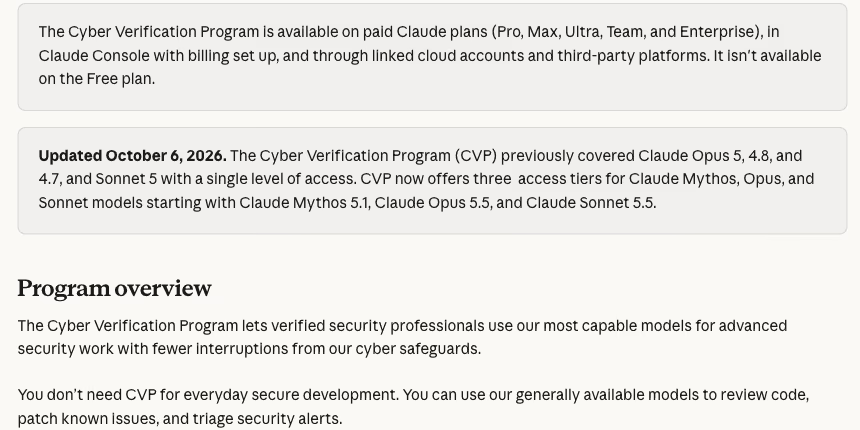 Anthropic's Cyber Verification Program article, captured 15 November 2026.
"You don't need CVP for everyday secure development. You can use our generally available models to review code, patch known issues, and triage security alerts."
Source: Claude Help Center
Our take: most Malaysian SMEs should skip it. Mythos earns its place in one case: Claude keeps refusing legitimate security work on systems you own. Say you need to test whether a flaw like PHP2Shell works against your own server, or pull apart a strange file found there.
It comes with strings attached:
- Data retention is on for everyone enrolled, so Anthropic can watch for misuse.
- Defense Access already needs two-step login. From 15 December 2026 it needs a sign-in that a fake login page can't steal, such as a passkey, and no long-lived API keys.
- On Max and Ultra, Mythos and Fable share up to 50% of your weekly usage. On Pro, Mythos runs only on usage credits.
For agencies, the rule that matters: individual access covers only you, as the application form said plainly. Gotchaa Lab's cybersecurity services for clients are separate, and this personal access is not used on them. Client work needs your company's own CVP approval plus a separate approval for external use, usually as a managed service.
Not sure whether Claude is blocking work you're allowed to do, or work you shouldn't? Let's chat.
General information only, not professional cybersecurity advice. Programme rules may change.